Skills
DevRel Strategy
How to structure, run, and measure developer relations programs. Covers DevRel org design, engagement tactics, aligning DevRel with business goals, measuring impact, building technical onboarding, and scaling community efforts. Drawn from practitioners at Twilio, Google Cloud, MongoDB, Apollo GraphQL, and others.
- +17
Monetizing Open Source
How to turn open source adoption and community into sustainable commercial revenue. Covers pricing models, packaging strategies, open core frameworks, the free-to-paid conversion, dual licensing, and managing community expectations through monetization changes. Drawn from practitioners at GitLab, dbt Labs, HashiCorp, and others.
- +19
Security Program Foundations
How to start and scale a security program at a startup: what to prioritize, where security sits in the org, how to build security culture, and when to hire a CISO. Drawn from practitioners at HashiCorp, Snyk, HackerOne, and others.
- +8
Security Incident Response
Preparing for, managing, and recovering from security incidents: breaches, attacker compromise, data exposure, and regulatory response. Covers incident response plans, breach communications, regulatory obligations, and forensics coordination. Drawn from practitioners at HackerOne, Splunk, and others.
- +1
DevSecOps Practices
Embedding security into the software development lifecycle. Covers shift-left security, security in CI/CD pipelines, vulnerability management, application security strategy, and building security-aware engineering teams. Drawn from practitioners at Snyk, GitHub, CircleCI, and others.
- +4
Content from the Library
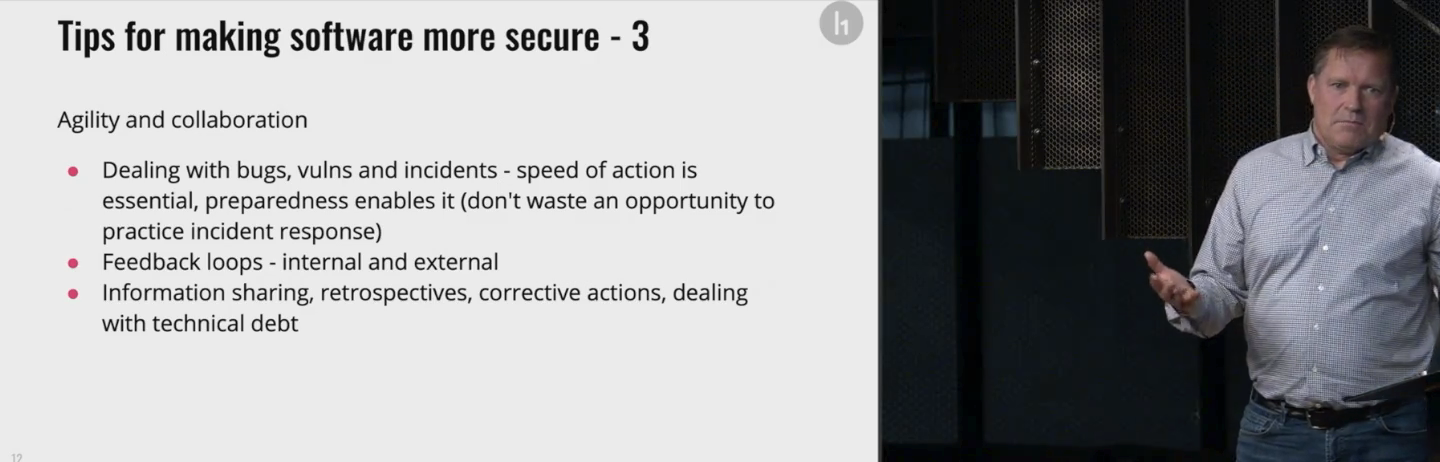
Building Securely for User Privacy
HackerOne CEO Marten Mickos discusses app sec strategies for building securely and ensuring user privacy from the earliest stages of your company. He also provides examples of different security models and processes at later-stage dev and enterprise software companies that you can integrate into your own company.

The Secure Developer Ep. #18, Collaborative Security with HackerOne’s Marten Mickos
In episode 18 of The Secure Developer, Guy meets with Marten Mickos, CEO of HackerOne, a platform for vulnerability coordination and a bug bounty program that helps developers test and build more secure systems.
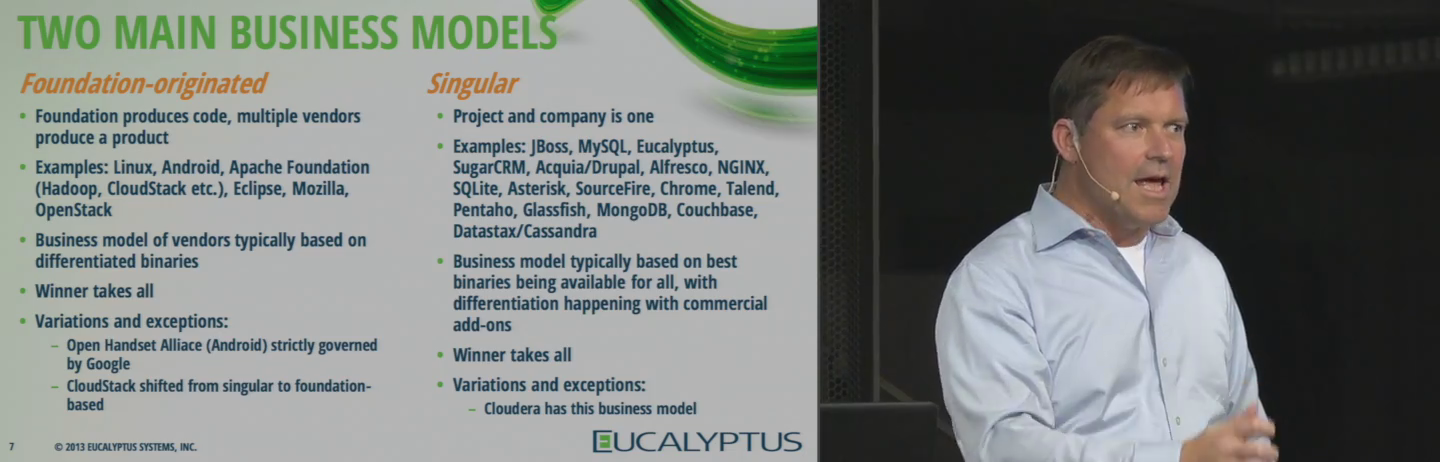
MySQL CEO on 2 Open Source Business Models
CEO of Eucalyptus.com and CEO of MySQL reviews the world of open source software – who is producing it, who is using it, and how they are turning it into a business. Using real-world examples, he will review various business models, looking at licensing, branding, governance, and proprietary add-ons to open source products.